Release 5.47
New in this release
This release introduces updates across authentication customization, identity verification, OIDC, passkeys, workload identities, directory sync performance, and portal usability.
Customizing the user authentication experience
This release introduces expanded controls to tailor the end-user authentication experience across branding, layout, messaging, language, and per-application sign-in behavior:
-
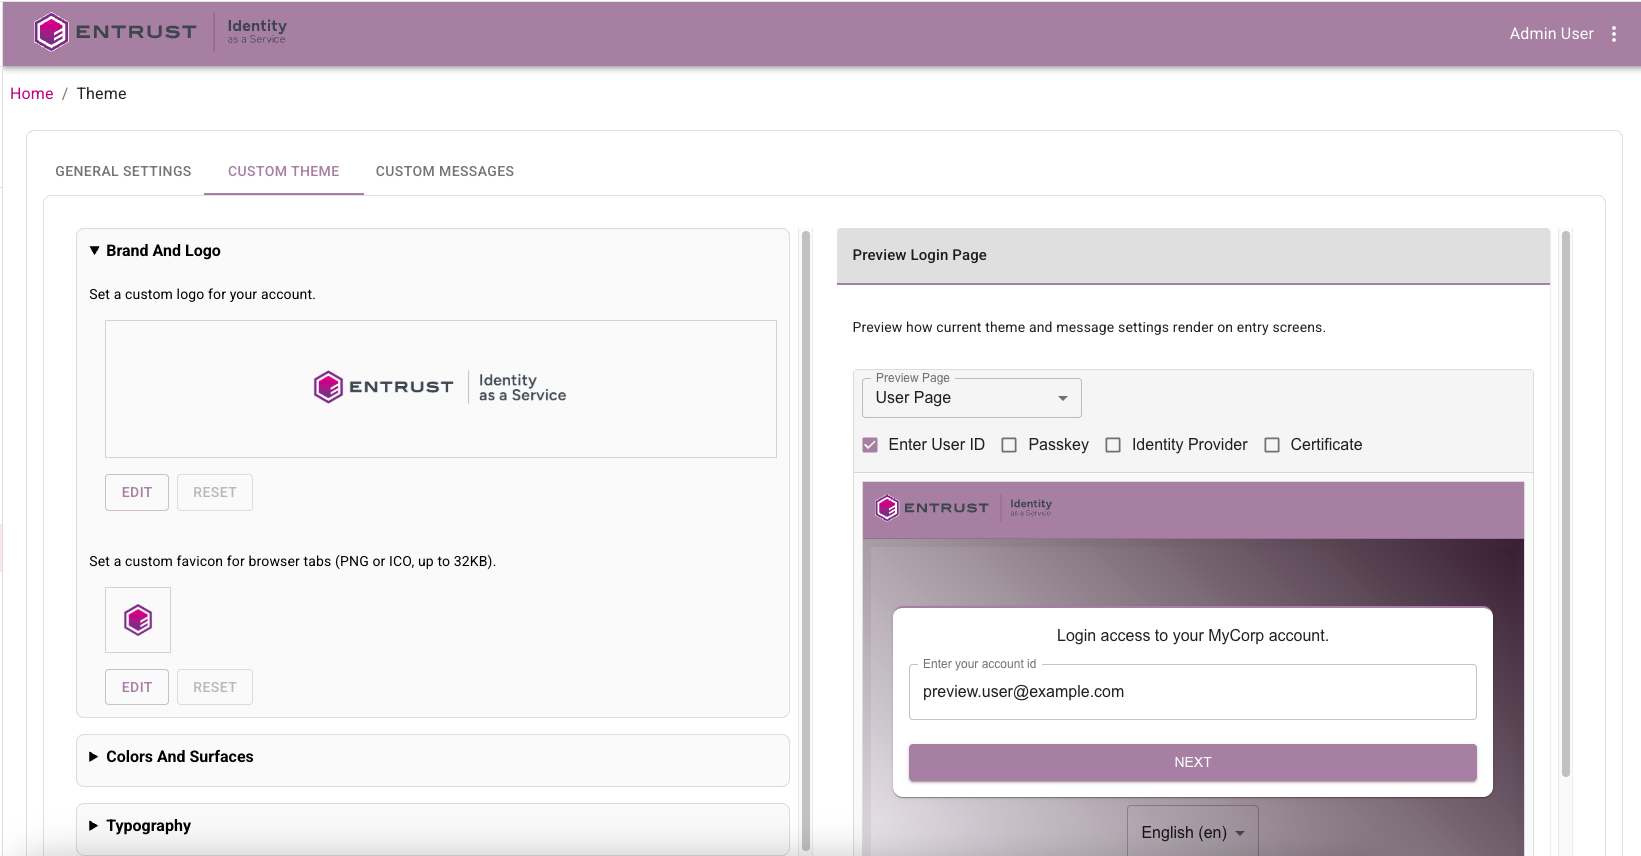
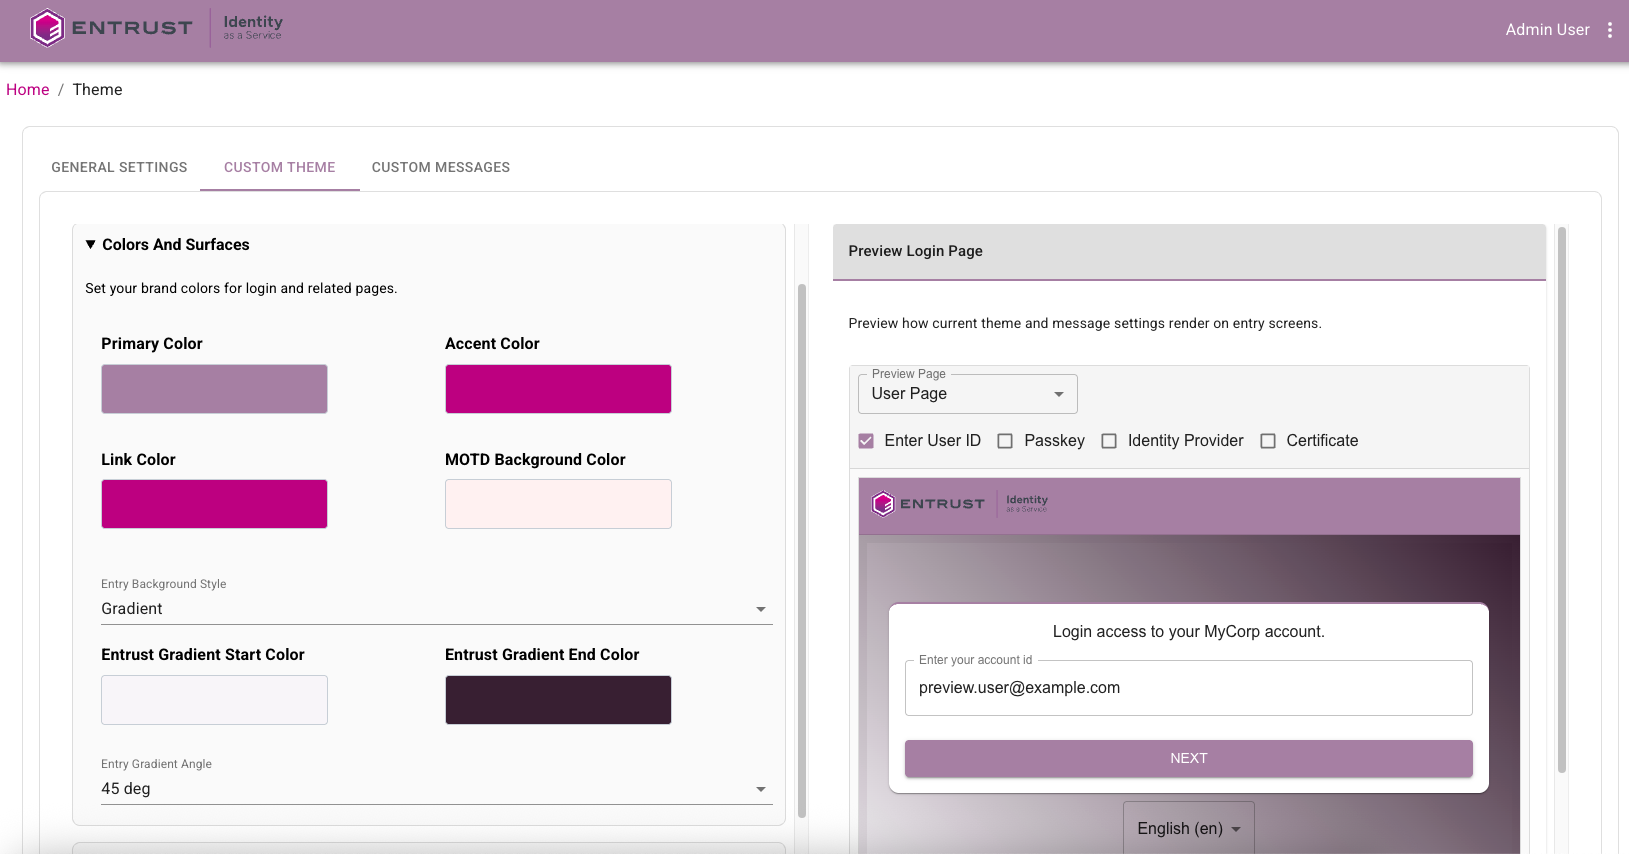
Brand and theme controls. Customize company logo and favicon, brand colors (including gradients), entry-page typography, and browser tab title for login-related pages.
-
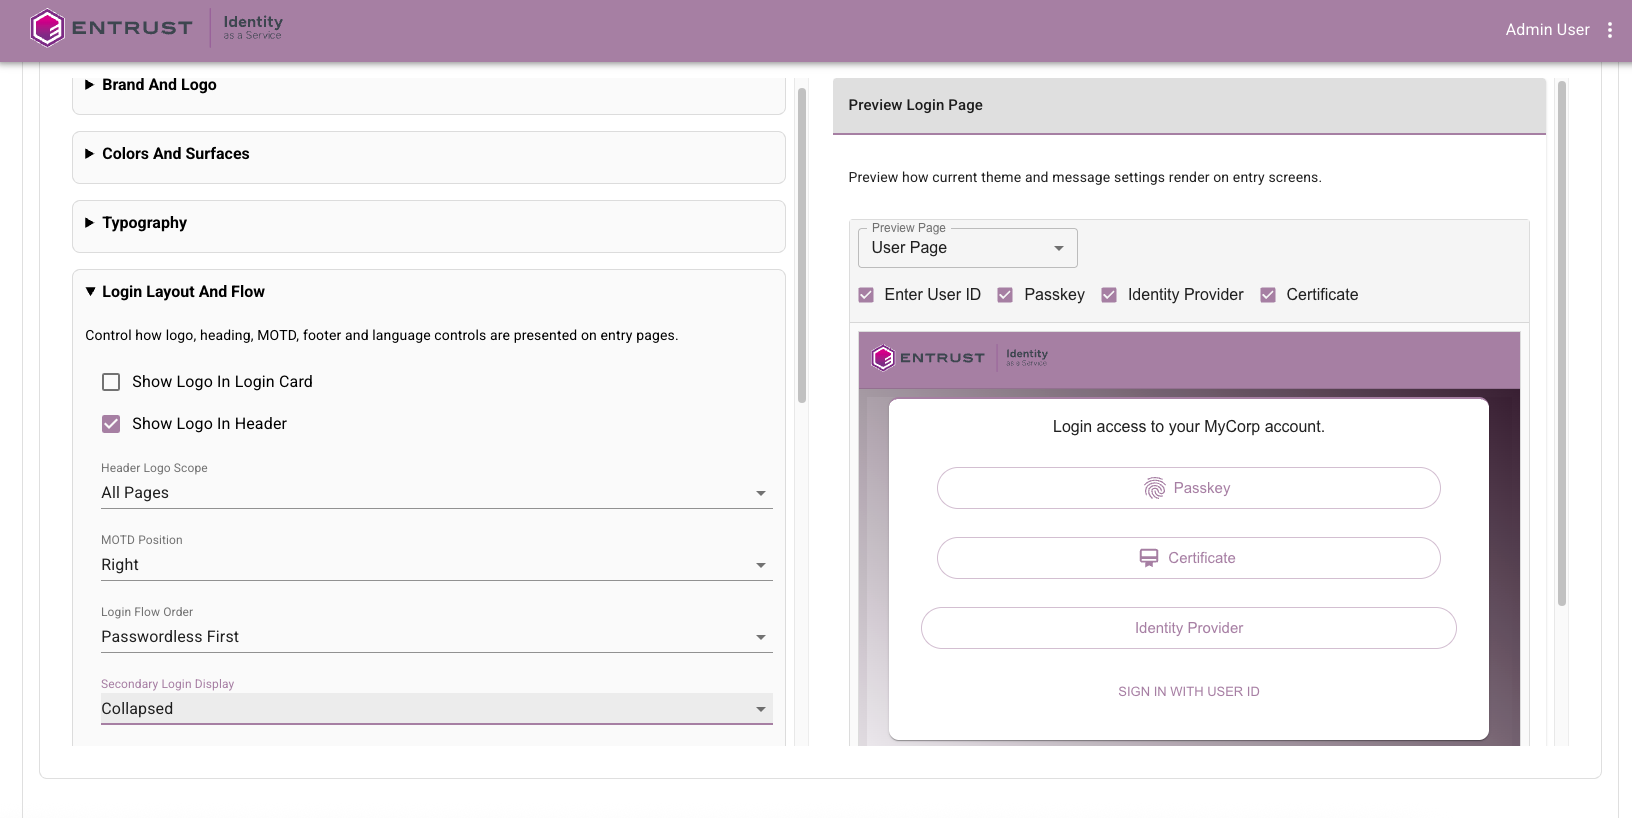
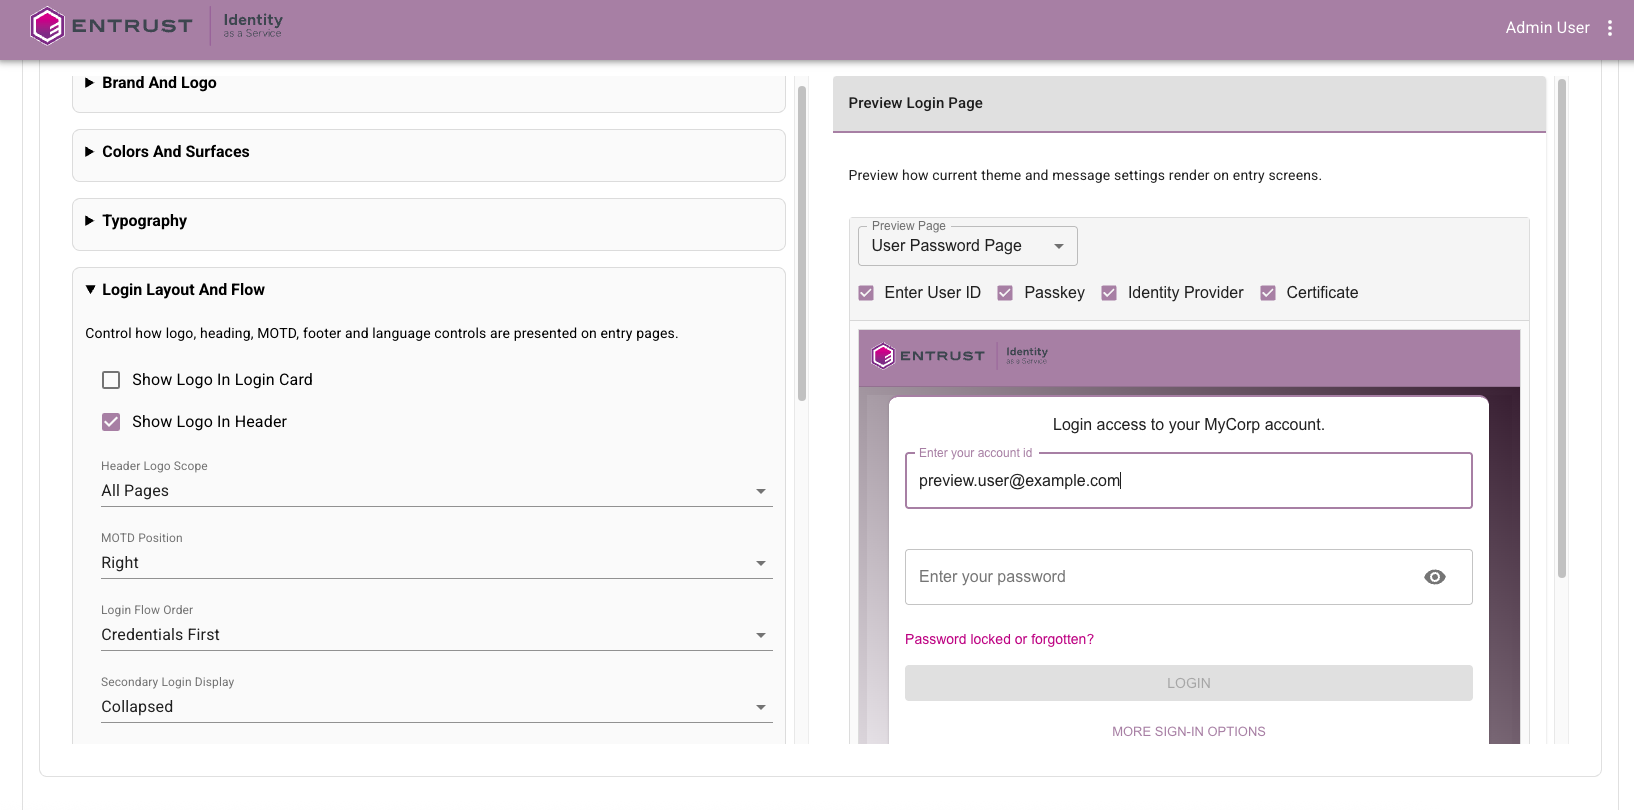
Login page layout and flow controls. Configure login card appearance, heading alignment, message-of-the-day placement, login flow order (credentials-first or passwordless-first), and collapsed secondary login options.
-
Per-application login optimization. For supported applications, optionally combine username and password onto a single page, control forgot-password link visibility for combined login, and enable user/administrator portal switching when experiences differ.
-
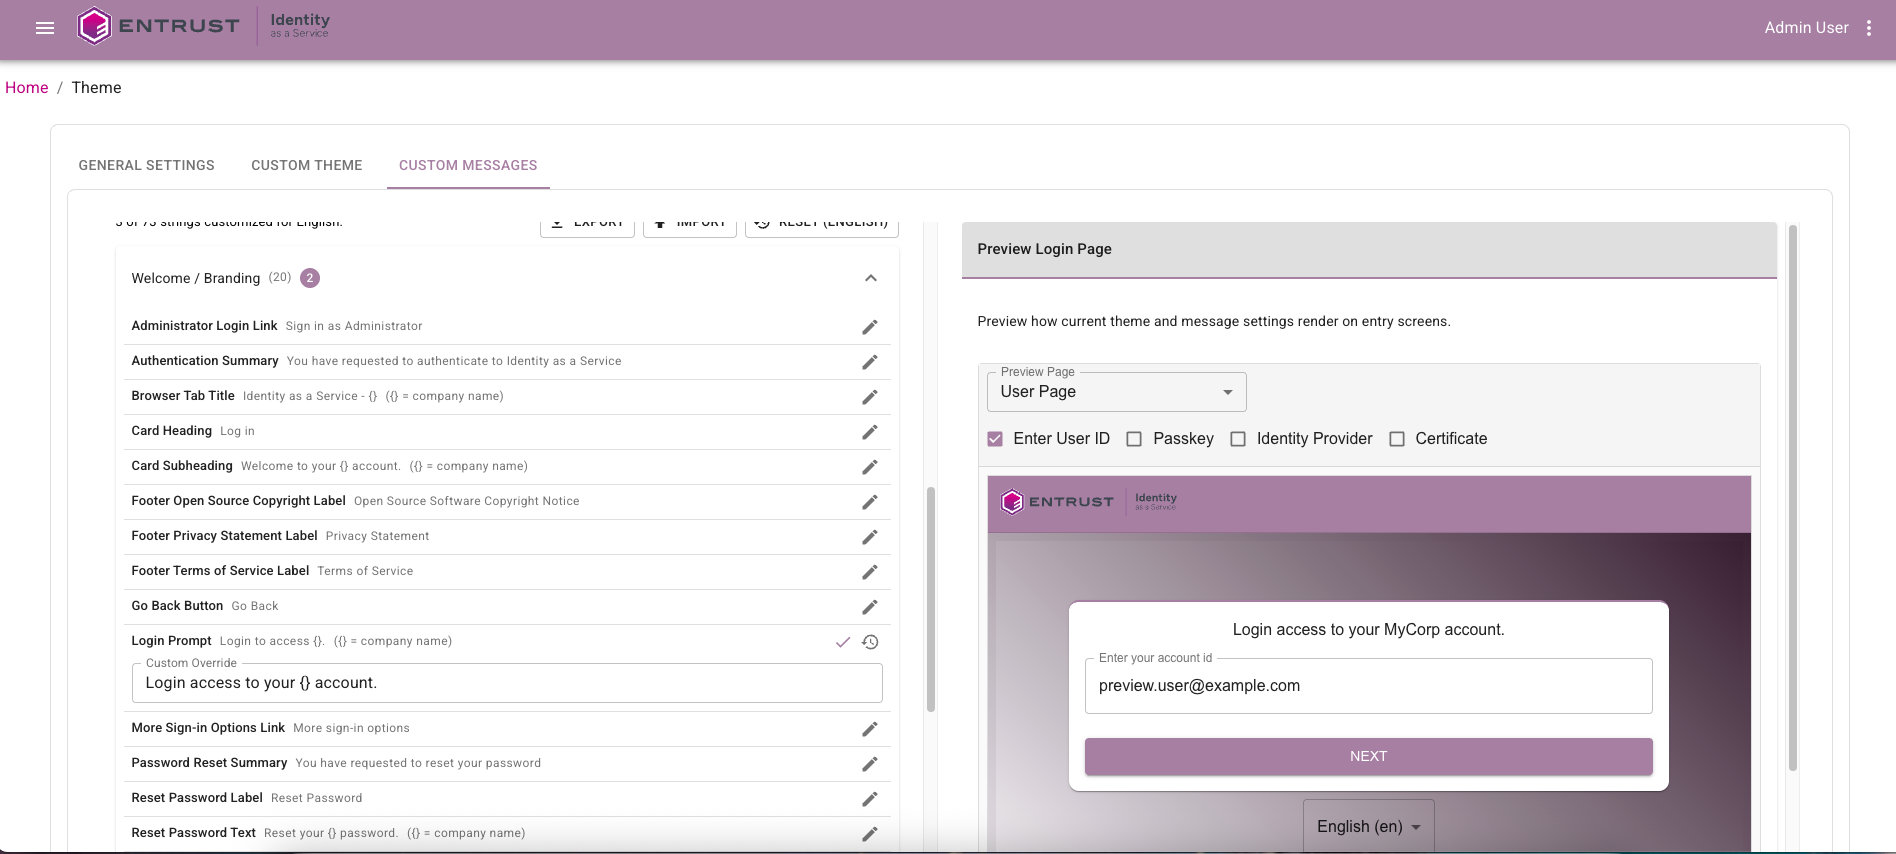
Custom login messages and localization. Override user-facing login strings, configure per-locale text, and manage large text updates with import and export JSON workflows.
-
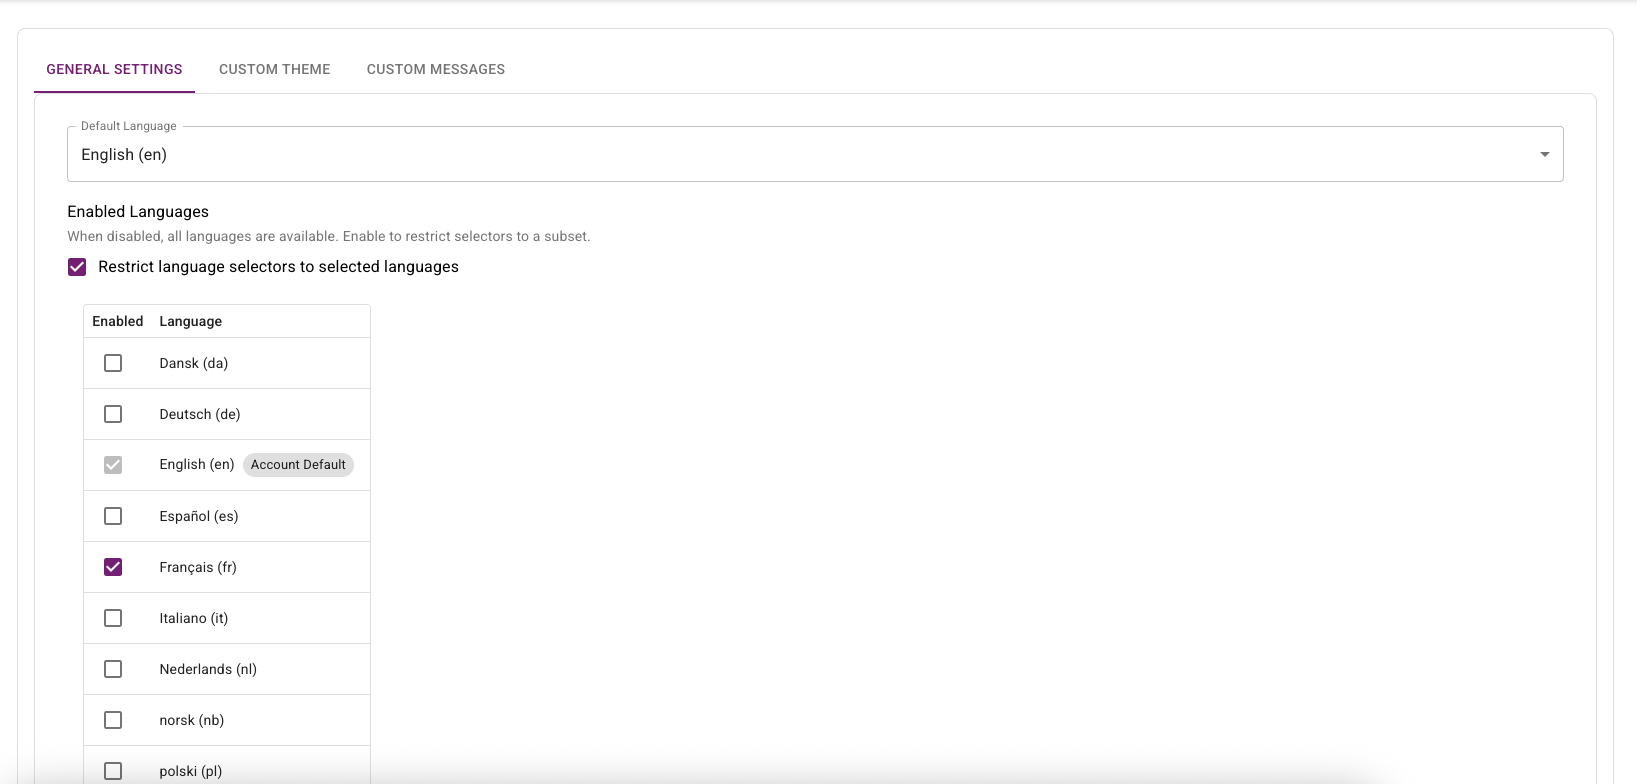
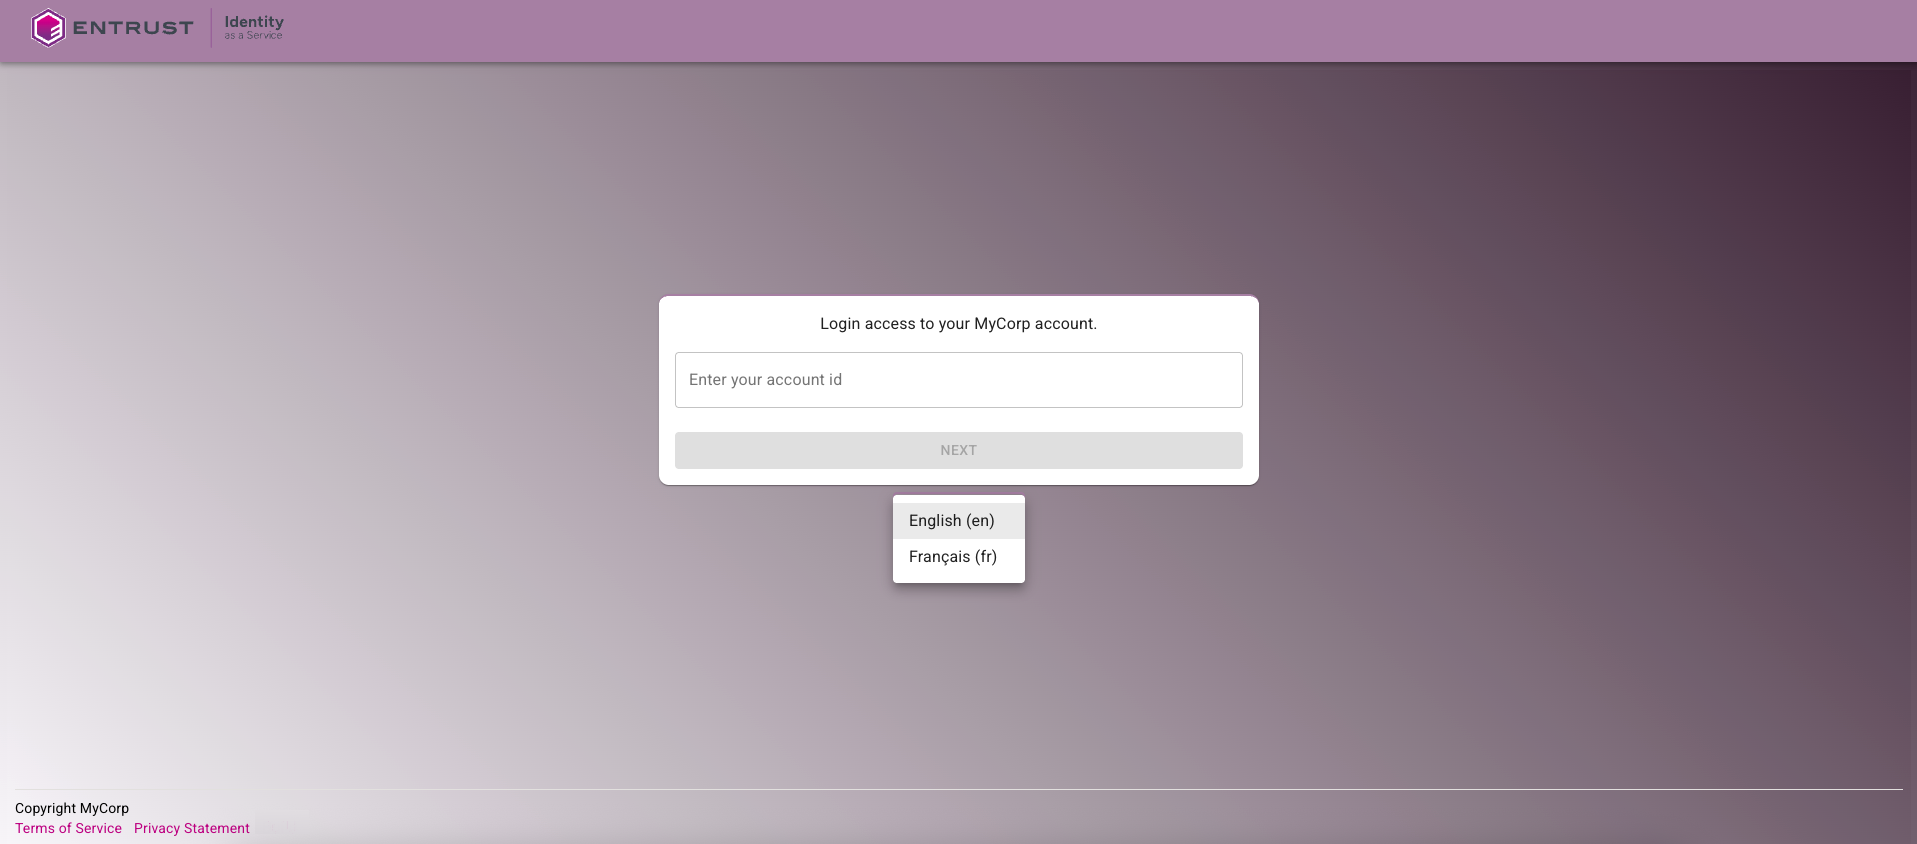
Multilingual experience controls. Restrict language selectors to supported locales and use account-default fallback behavior when unsupported locales are requested.
-
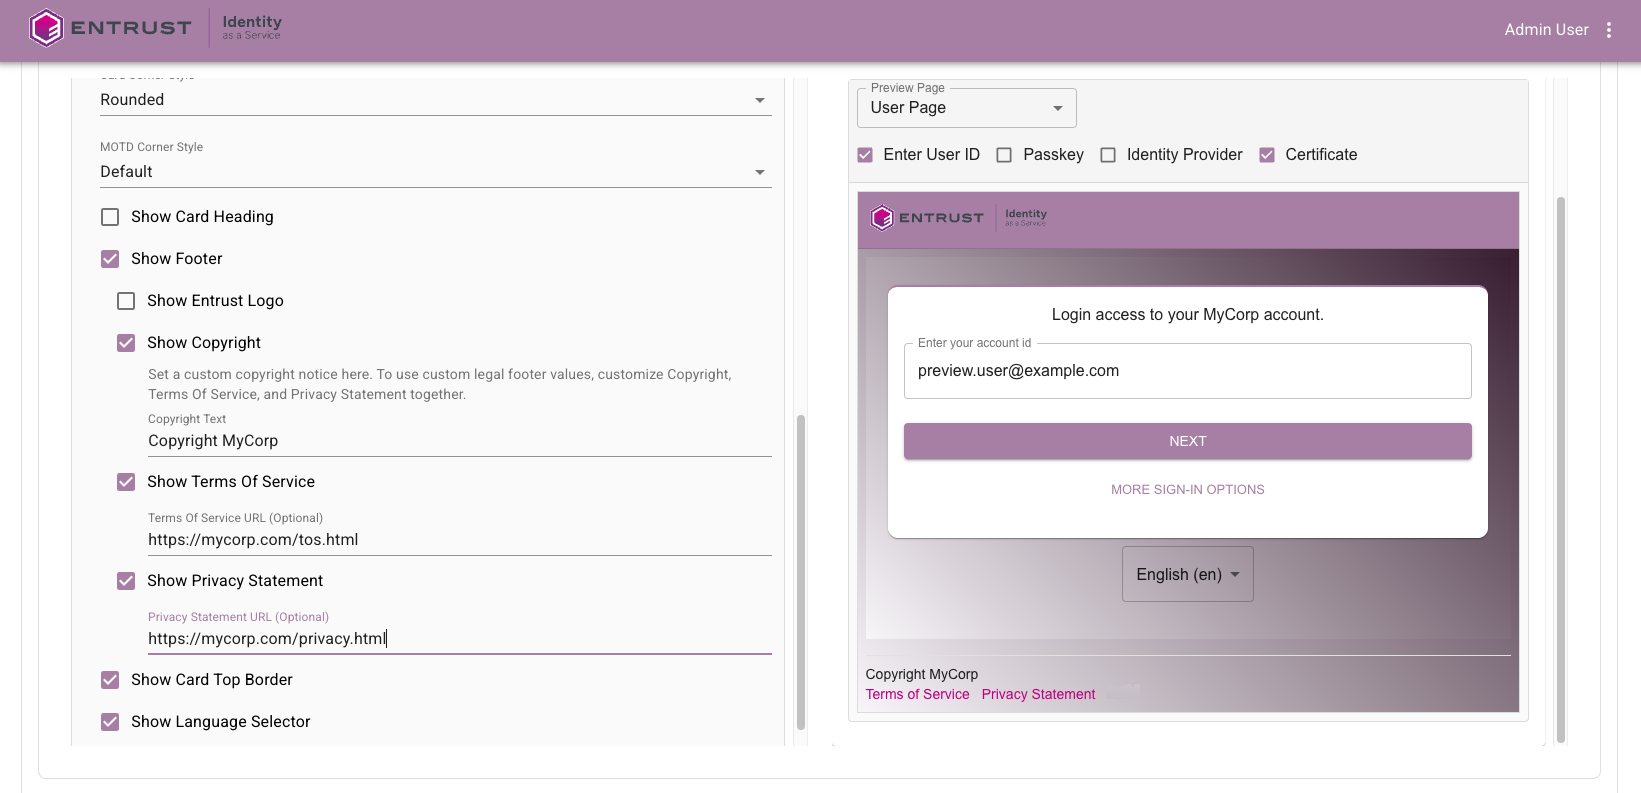
Footer and legal notice controls. Replace default footer legal items with organization-specific Terms of Service, Privacy Statement, and copyright, or hide footer elements as needed.
These enhancements let organizations align sign-in with brand and compliance requirements while reducing user friction. They also support clearer user guidance and stronger operational consistency across different applications and locales.
For overview and configuration details, see Customization.
Entrust IDV verification support
This release adds Entrust Identity Verification as a user verification option using document and biometric checks:
- Document plus biometric verification flow. Users can verify their identity during onboarding by scanning a government-issued ID and completing a facial recognition check.
- Policy-level enablement in user verification. Administrators can enable Entrust Identity Verification in Policies > Registration > User Verification, either as a standalone method or alongside SAML/OIDC Identity Provider verification.
- Automatic verified status and authenticator provisioning. On successful verification, user status is set to Verified and a Face Authenticator is automatically created for the user, reducing onboarding friction and preparing a reusable factor for future second-factor and account recovery scenarios.
- Web and mobile coverage. The verification experience is supported for both browser and mobile flows.
- Operational outcomes for review and failure. Verification outcomes include Verified, Under review, and Failed, with guidance for fallback verification when needed.
- Post-onboarding security use case. The automatically provisioned Face Authenticator supports later second-factor use cases, including password recovery.
These enhancements provide a higher-assurance verification path for organizations that need more than federated IdP verification alone, while also reducing user friction by automatically preparing a reusable biometric authenticator after onboarding that can be used for account recovery scenarios such as password recovery.
For overview, setup, and usage details, see Entrust Identity Verification.
OIDC and OAuth security enhancements
This release introduces OIDC and OAuth security enhancements and new configuration controls:
- PAR support (RFC 9126). Added support for Pushed Authorization Requests, including a PAR endpoint (
/api/oidc/par) for authorization code flows. Instead of sending full authorization request parameters in front-channel browser URL query strings, clients can send them over a back-channel request and use a shortrequest_uriduring redirect. - JAR support (RFC 9101). Added support for JWT Secured Authorization Requests so request parameters can be integrity-protected as signed JWT request objects.
- Expanded OIDC signing algorithm and key support. Added support for RSA-PSS (
PS256,PS384,PS512) with RSA keys, and Elliptic Curve keys with ECDSA algorithms (ES256,ES384,ES512) for OIDC request and token signing scenarios. You can also require specific accepted signing algorithms for signed request inputs. - DPoP support (RFC 9449). Added Demonstrating Proof of Possession support to bind tokens to client key material and reduce token replay risk if tokens are intercepted.
- IDaaS Authentication JavaScript SDK DPoP support: Added DPoP support in the IDaaS Authentication JavaScript SDK for OIDC flows. For SDK documentation, see https://github.com/EntrustCorporation/idaas-auth-js.
- Expanded token endpoint client authentication options. Added support for additional client authentication and credential configuration options, including
private_key_jwt,spiffe_jwt, and managed key material throughjwks_urior inline JWK/JWKS. - New OIDC application security settings. Added configuration options for client authentication and request hardening, including Private Key JWT, JWKS URI or inline JWK/JWKS, cryptographic signing algorithm selection (including JAR signing algorithms), PAR mode and format controls, and DPoP sender-constraint options.
These changes strengthen request integrity, reduce front-channel data exposure, and improve token theft resistance. Together, they provide stronger default security for OIDC integrations and give administrators clearer controls to enforce higher-assurance client behavior.
For implementation details, see OAuth and OIDC enhanced security features.
Workload identity and SPIFFE OIDC client authentication
This release introduces first-class workload identity support for non-human identities (for example, service accounts, microservices, AI agents, and CI/CD workloads) and adds SPIFFE JWT-SVID support for OIDC client authentication.
- Workload identity lifecycle support. Added workload identity create, view, update, and delete APIs with role-based permissions for workload management operations.
- Admin portal workload management UI. Added a dedicated Workload Identities experience with list and detail views, active and inactive state control, owner and group assignment, OIDC settings, claims mapping, and workload-linked audit visibility.
- Workload OIDC authentication options. Workload identities use OIDC client credentials flows and can be configured with supported token endpoint client authentication methods, including the new
spiffe_jwtoption. - SPIFFE JWT-SVID authentication method. Added SPIFFE JWT-SVID (
spiffe_jwt) as an OIDC token endpoint client authentication method for workload and machine-to-machine scenarios. - Workload runtime controls and audit visibility. Added inactive workload enforcement, workload last-authentication tracking, and enhanced workload authentication auditing, including SPIFFE ID context when applicable.
- Expanded workload claim mapping. Added workload-oriented claim mapping sources, including group-derived values, workload identity attributes, and SPIFFE ID.
These enhancements provide stronger controls for machine identity lifecycle management while improving workload authentication assurance and auditability in OIDC client credentials flows. SPIFFE support is significant because it adds trust-domain and SPIFFE ID pattern validation for machine identities, which strengthens authentication assurance and improves audit traceability.
For an overview and configuration details, see Workload identities. For a customer-focused look at how SPIFFE and DPoP work together to reduce replay risk, see How SPIFFE and DPoP reduce credential theft risk for modern workloads.
Passkey policy and attestation controls
This release adds stronger policy controls for which passkeys can be registered and used for authentication.
- Authenticator restrictions. You can allow all authenticators, allow only selected authenticator models, or block selected authenticator models. Model-level restrictions are based on authenticator identity metadata provided by the FIDO Alliance Metadata Service, so you can define exactly which passkey types are permitted in your tenant.
- Unknown authenticator handling. You can control whether authenticators that are not recognized in trusted metadata are allowed or blocked.
- Device-bound enforcement. You can require device-bound passkeys and block synced passkeys where needed.
- Expanded policy guidance. The Passkey/FIDO2 policy guidance now helps administrators choose a policy posture, understand security and compatibility tradeoffs, and plan rollouts for user verification, device-bound passkeys, attestation, authenticator restrictions, and non-compliant authenticator enforcement.
These controls are important because they let you enforce your organization's passkey trust requirements, reduce risk from untrusted or non-compliant authenticators, and align passkey usage with security and compliance policy.
For policy setup details, see Configure Passkey/FIDO2 authenticator settings.
Directory synchronization delta sync enhancements
Delta sync is now the default for scheduled on-premises Active Directory synchronization runs. This release also introduces clearer synchronization mode controls so administrators can choose between Delta and Full sync when they run Force sync.
Delta sync means IDaaS does not run a full directory scan on every run. Instead, it reads only objects that changed since the last successful synchronization (for example, newly created users, updated attributes, membership changes, or disabled accounts).
This is useful because most directory data does not change between synchronization runs. By processing only changed objects, IDaaS completes scheduled synchronizations faster, generates less load on LDAP and network infrastructure, and reduces the chance that long-running full directory scans overlap with business-hour operations. It also lets you run synchronization jobs more frequently, so directory updates are reflected in IDaaS more quickly.
This release includes the following Active Directory synchronization improvements:
- Delta sync is now the default for scheduled Active Directory synchronization runs. IDaaS processes only changed directory objects since the previous checkpoint.
- Force Sync now supports both Full and Delta modes for on-premises Active Directory. Use Full for a complete directory scan, especially after configuration changes, and use Delta for incremental synchronization.
- Improved synchronization efficiency. Processing only changed objects reduces LDAP and network load, decreases payload size, and improves synchronization runtime.
- Clearer operational recovery path. If a user fails synchronization because required attributes or identifiers are invalid, update the user in Active Directory and the next delta sync can process that corrected change.
For configuration details, see Delta sync and full sync for Active Directory.
User portal redesign and authenticator flow improvements
This release redesigns the user portal profile experience and improves core self-service workflows for activity review, authenticator management, and registration reliability.
-
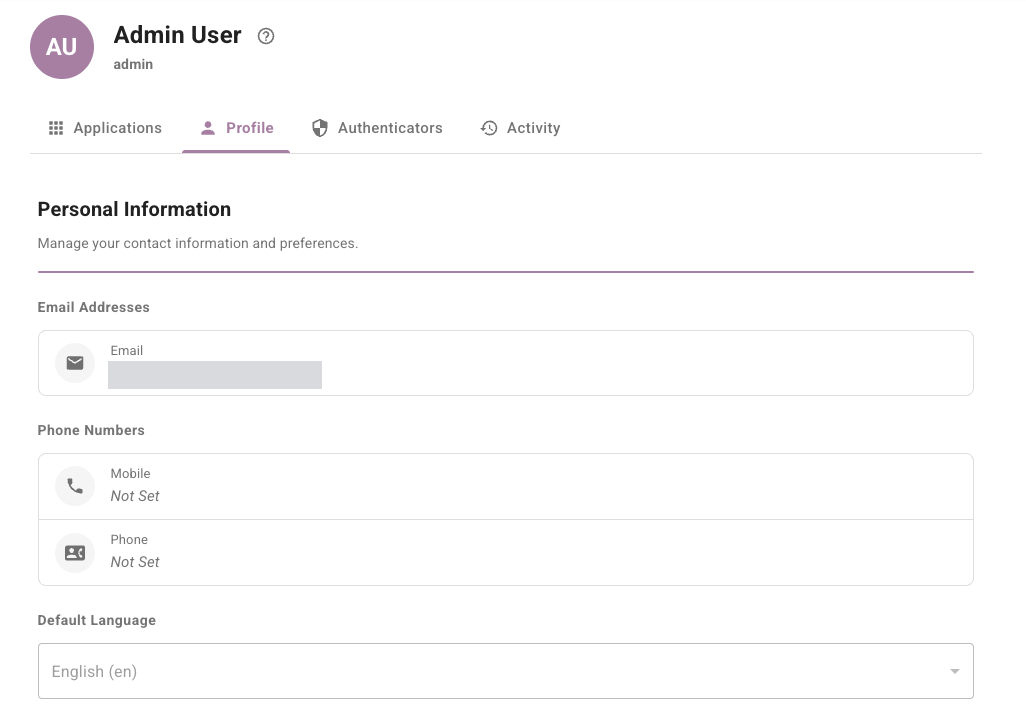
New user portal profile shell and navigation. Introduced a consistent profile page design across user portal profile sections, with a profile header and horizontal tab navigation, so navigation is simpler, pages behave more consistently on mobile and desktop, and accessibility is improved.
-
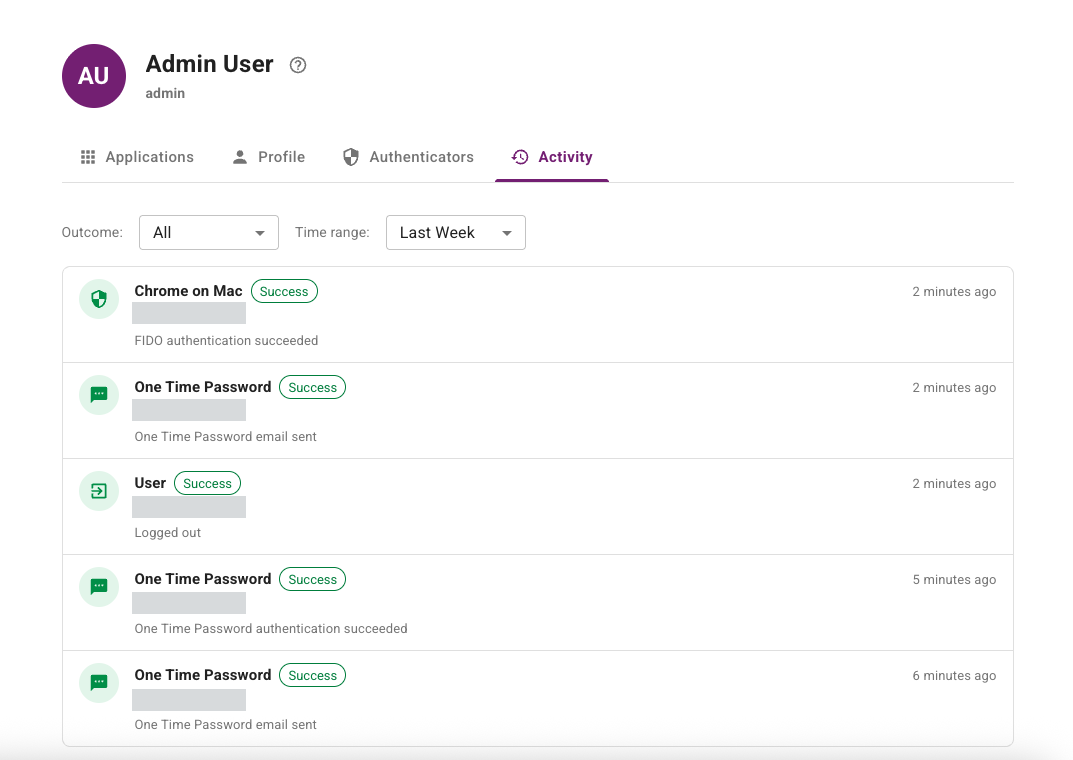
Redesigned activity experience. Moved activity into an integrated profile tab with outcome filters, time-range filters, pagination, and improved event readability.
-
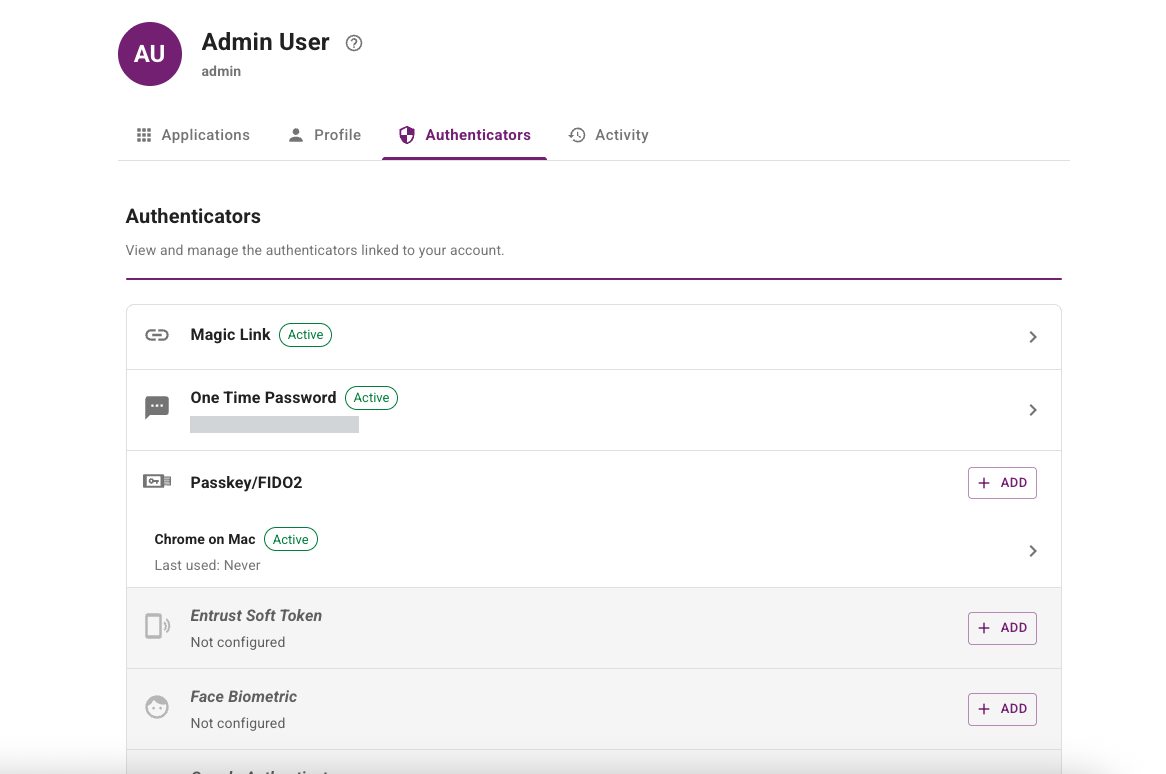
Modernized profile and authenticator management pages. Updated profile and authenticator experiences with newer UI patterns and improved consistency across flows.
-
Passkey registration improvements. Updated registration behavior, including support for automatic passkey naming.
For a User Portal overview and links to configuration procedures, see User Portal settings.
Administration portal dashboard analytics and audit investigation improvements
This release modernizes the Administration portal dashboard and improves how administrators investigate and filter audit activity.
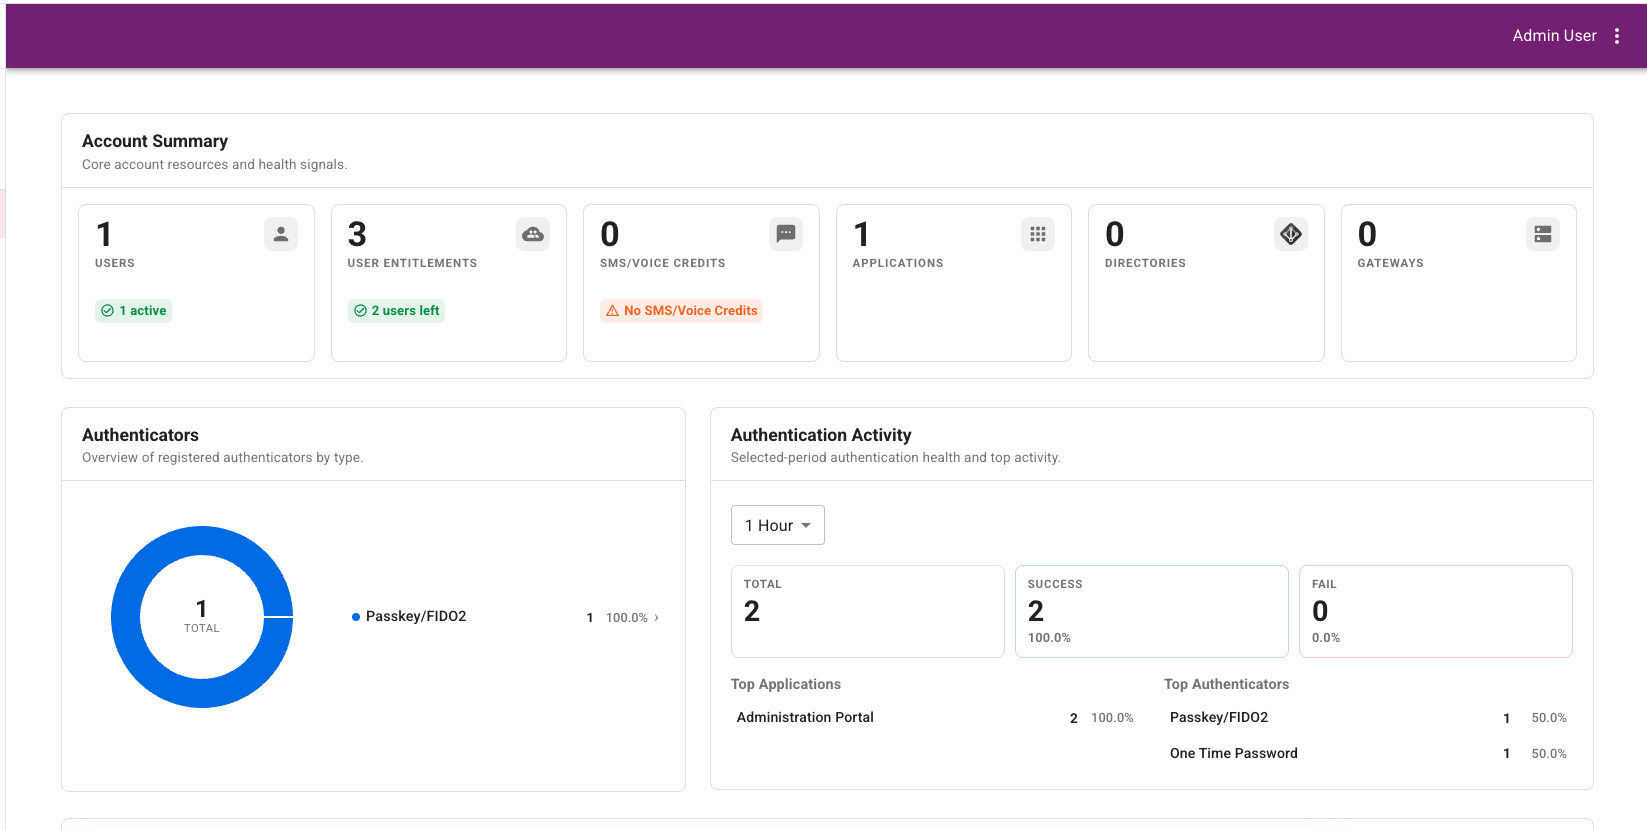
- Dashboard layout refresh. Updated visual hierarchy and section layout across Account Summary, System Alerts, Authentication Activity, and Recent Activity to improve readability and at-a-glance monitoring on desktop and mobile viewports.
- New Authentication Activity panel. Added selected-period metrics for total, successful, and failed authentications with success and failure percentages, plus ranked Top Applications and Top Authenticators views.
- Drill-down investigation workflow. Added one-click drill-down from Authentication Activity entries into pre-filtered audit results to speed up investigation.
- Authenticator insights improvements. Updated authenticator distribution visualization with more stable chart color behavior and improved empty-state handling.
- Audit details experience upgrade. Replaced the previous audit details dialog with a right-side details drawer that provides richer grouped event context, quick field-level filtering actions, and copy-all event details.
The first screenshot shows the updated dashboard analytics experience. The second screenshot shows the updated audit investigation experience.
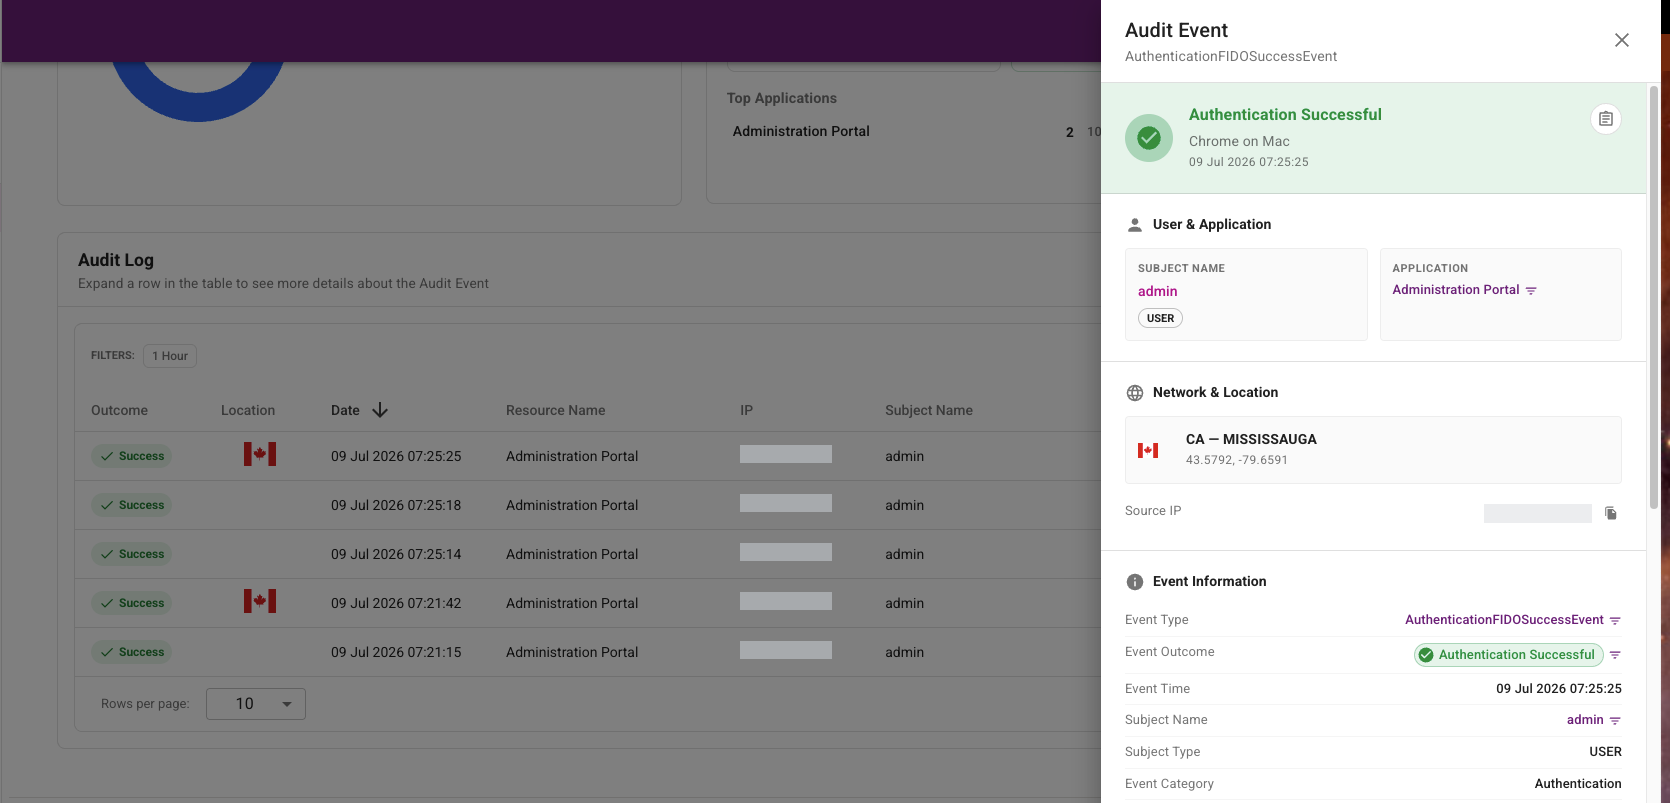
For dashboard and audit workflow details, see Dashboard and View and export audit logs.
Documentation updates
This release also includes documentation updates that make existing configuration and operational guidance easier to find and use:
- Accessibility conformance report. Added the current Accessibility Conformance Report (ACR), created from the Voluntary Product Accessibility Template (VPAT), which documents how IDaaS conforms to accessibility standards and helps organizations evaluate accessibility and procurement requirements. See Accessibility.
- System requirements. Added supported TLS versions and cipher suites, production egress IP addresses for server-initiated outbound requests from IDaaS, and updated Entrust Identity Verification SDK version information. See Requirements.
- External risk engines. Expanded guidance for external risk engine scenarios, including risk signal categories, transaction details, connector setup, placeholders, request mapping, response extraction, and risk assessment rules. See Manage external risk engines and Configure connector-based risk engines.
- Resource rules. Expanded resource rule guidance with clearer explanations of access filters, risk evaluation, authentication flow selection, strict access behavior, common rule patterns, and troubleshooting for access denial. See Create and manage resource rules.
- Authenticator planning. Added an authenticator selection guide to compare available authenticators, deployment considerations, recovery effort, deployment patterns, and assurance-level recommendations. See Authenticator selection guide.
- Account recovery planning. Added guidance for planning account recovery and authenticator readiness across password reset, help desk verification, user unlock, first-time authenticator registration, User Portal self-management, and Face Biometric recovery after Entrust Identity Verification. See Account recovery and authenticator readiness.
- Application integration procedures. Refined SAML, OIDC/OAuth, RADIUS, and API application integration procedures for clearer setup flow and navigation. See Manage applications.
- Login options. Added reference guidance for application sign-in method support, selection behavior, and related User Login settings. See Manage login options.
- Directory synchronization. Added a directory synchronization overview with key concepts, synchronization scheduling, Force sync behavior, full and delta synchronization modes, Active Directory delta sync defaults, and guidance for choosing Full sync after configuration changes. See Manage directory synchronization.
- OIDC and OAuth foundations. Added supporting pages for OAuth/OIDC basics, examples and tokens, and token validation best practices. See OAuth and OIDC foundations.
- Identity Provider and migration guidance. Updated generic OIDC Identity Provider and migration documentation for clarity and correctness. See Identity Providers and Migration.
- Audit log reference. Added entity type descriptions, expanded the authentication event reference, and documented management event types. See View and export audit logs.
Fixed or changed in this release
- Restored the View Scopes action in the Users List action menu when prerequisites are met. (42060)
- Fixed missing audit attribute details for embedded OIDC application refresh token grant-type settings. (41685)
- Resolved an audit logging error that occurred in specific automated test scenarios. (42131)
- Fixed intermittent 503 errors during Microsoft Entra ID sign-in. (42372)
- Fixed a 503 sign-in error that occurred in specific account configurations. (42336)
- Corrected authenticator status display for AD connector users whose password state is locked. (42381)
- Fixed duplicate audit generation when updating AD sync group filters and desync policy settings. (40787)
- Prevented saving SAML assertion encryption settings when no encryption certificate is loaded. (40763)
- Fixed an error when adding a user password in cases where email is unavailable. (38685)
- Added support for HTTPS localhost URIs as OIDC redirect and logout URIs for local development scenarios. Previously, only HTTP URLs were supported for localhost. (42230)
- Fixed Assigned Token filtering when Date Last Used is set to Never. (42199)
- Fixed an issue where, after navigating to any page other than the first page of a list and performing an action that opens another page, the list did not refresh correctly when returning. (40828)
- Restored missing audit events for specific IdP authentication failure paths. (41686)
- Restored missing group details in bulk hardware token import audit events. (41026)
- Fixed bulk user operation filtering so Set User results are returned correctly. (37694)
- Fixed client IP audit logging for authentications through vanity URLs so the originating client address is captured correctly in audit events. (41845)
- Fixed custom date and time filtering behavior for hardware token data. (28385)
- In the audit list, EQUALS is now set as the default operator for all applicable filter fields. (38448)
- Updated permission handling so users without directory permissions are blocked in the UI from accessing AD connector synchronization pages, instead of encountering an error. (42200)
- Fixed 1Password autofill submission behavior on login challenge screens. (42617)
- Fixed missing localization for password email notification
serialNumberandIdentifierfields. (41852) - Fixed missing localized Welcome Subscriber email templates for service provider accounts. (40651)
- Fixed missing localization for the duplicate webhook name error message. (42157)
- Fixed registration and login flows so the selected language is honored instead of reverting to the user's profile language. (41975)
- Fixed a 500 error for invalid phone challenge data in AD sync OTP voice flows. (42540)
- Clarified token recovery actions by updating Token Unlock labeling to Token PIN Unlock in relevant user and administrator flows. (42378, 42379)
- Fixed managed-role profile visibility when users belong to both managed and unmanaged groups. (41692)
- Fixed field alignment issues on the Policies > Authenticators page in Microsoft Edge. (41412)
- Fixed a null pointer error when minimum password lifetime is enabled and last-changed time is missing. (42527)
- Fixed a save issue in resource rule configuration after clearing country search in geolocation settings. (40603)
- Fixed a null pointer error when loading applications for the current user. (42364)
- Improved passkey Windows Hello icon visibility against default backgrounds. (42525)
- Fixed portal redirect behavior when the hostname cannot be found. (35078)
- Improved account-name encoding for Google and Microsoft Authenticator provisioning. (42573)
- Disabled unavailable Provisioner page actions for the auditor role. (40620)
- In Smart Credential hardware settings, renamed SC Hardware Best Option to Best Available. (34538)
- Fixed duplicate email notifications for locked users when both user notifications and locked-email settings are enabled. (42521)
- Corrected a typo in the Require Consent label for the OIDC and OAuth Generic Web Application template. (41930)
- Fixed saving RBA rules when geolocation risk factors are selected and country search text is cleared. (41071)
- Fixed saving modifications to the Google token activation email template. (42172)
- Improved push-notification failure handling for Entrust Soft Token: IDaaS now stops trying to deliver push notifications after prior delivery failures, including common non-recoverable cases such as a token removed from the mobile app or the app removed from the device. If delivery needs to resume for that token, administrators can perform a token reset; if delivery fails again, push is disabled again for that token. (41986)
- Corrected entitlement grace-period warning timing. (42036)
- Removed obsolete User Set Bulk operation options that were still shown in the UI. (42383)
- Fixed audit entity-name display for user password unlock events. (42368)
- Extended the configurable inactivity threshold period from 365 days to 1,095 days. (41961)
- Improved password reset rule validation for current-password checks. (42377)
- Added distinct AD and LDAP directory-type indicators in both directory list and directory details (add/edit) pages. (42280, 42435)
- Fixed Password Reset Magic Link option display for non-default named password settings in group policy. (42511)
- Fixed disable behavior and messaging for locked Entrust Soft Token and Google Authenticator, including corrected confirmation and email wording. (42352)
- Fixed deletion handling for smart credentials associated with decommissioned certificate authorities. (42339)
- Fixed eGrid save failures in specific browser scenarios. (40871)
- Disabled submission for managed-role updates of unassigned grid cards and tokens when no group is selected. (38867)
- Fixed authentication flow name visibility for read-only permission scenarios. (40877)
- Increased the maximum number of named passwords allowed from 5 to 20. (42974)
- Fixed a save issue that prevented some users from updating Override Authenticator Preference settings. (42428)
- Improved label layout on the Bulk Import IDE migration add page. (42146)
- Fixed an incomplete Change Password experience that prevented users from saving password changes in specific flows. (42513)
- Updated IDaaS Portal sign-ins through Identity Providers so OIDC and SAML requests use the configured Identity Provider max age instead of a separate portal default. (42928)
- Fixed face biometric registration selection so expired, unregistered face biometrics are not considered when choosing a face biometric to register. (41287)
- Status for AD Password shows Change Required when Active Directory requires the user to change their password at next sign-in. (42575)
Changes to Identity as a Service (IDaaS) APIs
Authentication API
New operations
- None.
Removed operations
- None.
Changed operations
- None.
Changed models
UserAuthenticateQueryParameters- Added:
response(string) - Added a response parameter used with the combined user ID and password authentication mode.
- Added:
Administration API
New operations
GET /api/web/v1/settings/fido/authenticators (listAuthenticatorsUsingGET)- List FIDO authenticators.
Removed operations
- None.
Changed operations
- None.
Changed models
FIDOAuthenticatorModel- Added: New schema representing FIDO authenticator model metadata used by passkey authenticator trust-policy configuration.
FIDOAuthenticatorSettings- Added:
authenticatorTrustMode(string) - Defines how authenticator trust is evaluated. - Added:
authenticatorList(array) - List of authenticator models used for allow or deny policy decisions. - Added:
unknownAuthenticatorPolicy(string) - Defines how unknown authenticator models are handled. - Added:
nonCompliantAuthenticatorPolicy(string) - Defines how non-compliant authenticator models are handled. - Required added:
authenticatorTrustMode,unknownAuthenticatorPolicy,nonCompliantAuthenticatorPolicy.
- Added:
FIDOAuthenticatorSettingsParms- Added:
authenticatorTrustMode(string) - Defines how authenticator trust is evaluated. - Added:
authenticatorList(array) - List of authenticator models used for allow or deny policy decisions. - Added:
unknownAuthenticatorPolicy(string) - Defines how unknown authenticator models are handled. - Added:
nonCompliantAuthenticatorPolicy(string) - Defines how non-compliant authenticator models are handled.
- Added:
DirectorySync- Added:
deltaCrawl(boolean) - Indicates whether directory synchronization runs in delta mode. - Added:
forceCrawlSequence(integer) - Tracks force-crawl sequence handling for synchronization workflows.
- Added:
Enterprise Service Gateway (ESG) Deprecation
Entrust supports the last four releases of the Enterprise Service Gateway (the current version 5.47 and the three previous releases 5.44, 5.45, and 5.46, which includes 5.46.1). Entrust recommends that customers always upgrade their Enterprise Service Gateway to the latest release because each release contains security updates to the Enterprise Service Gateway Operating System.
In an upcoming release, changes are planned that will break versions of ESG older than 5.33.